

Liability for officials, cyber hygiene classes in schools, national SOC centers. What tasks is Uzbekistan setting for itself in the field of cybersecurity?
By the end of 2026, a draft law will be developed in Uzbekistan establishing liability for officials who are indifferent to cybersecurity requirements. By the end of 2029, national SOC centers will be launched in the country. Work on introducing cyber hygiene classes in schools will be continued systematically.
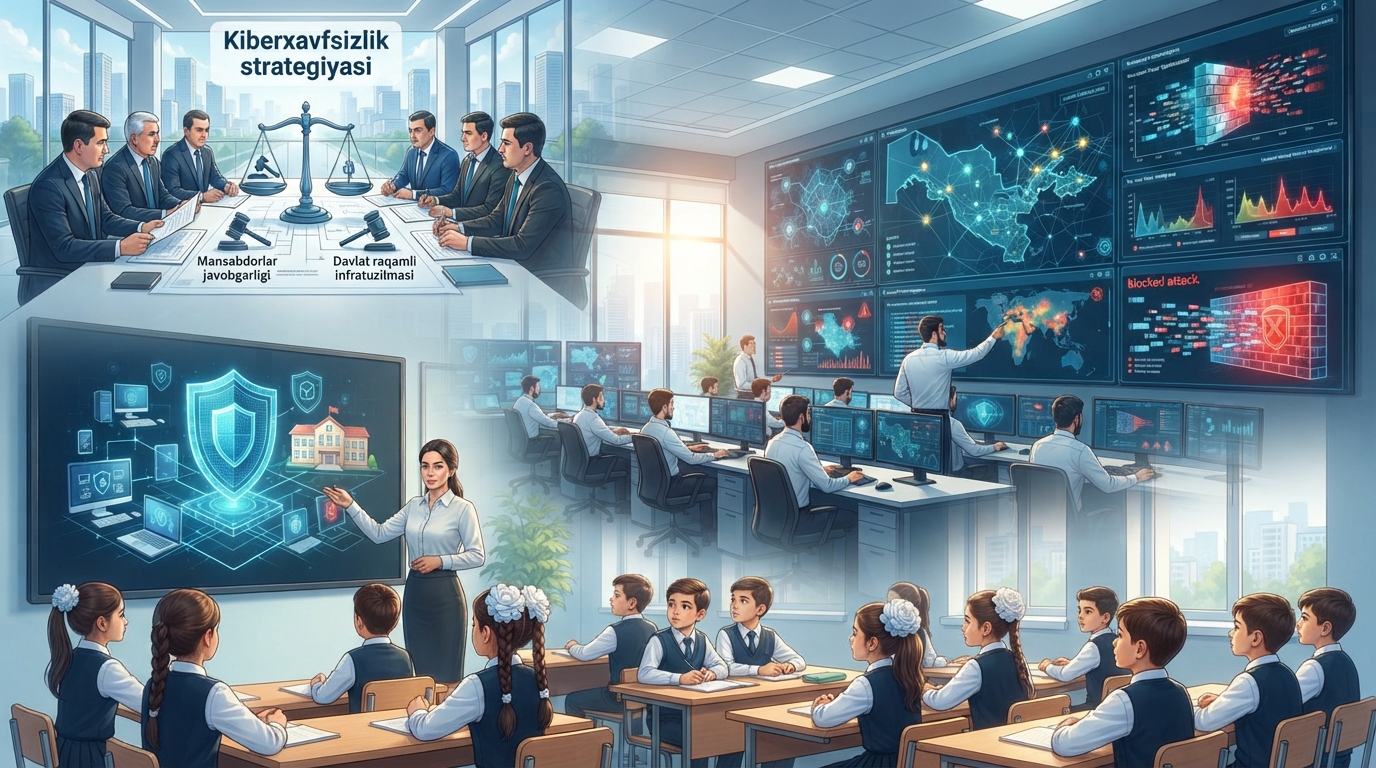
Liability for officials, cyber hygiene classes in schools, national SOC centers. What tasks is Uzbekistan setting in the field of cybersecurity?
Speaking about digital infrastructure in Uzbekistan, Olimjon Mirzayev touched upon the issue of national cybersecurity in detail, calling it one of the main pillars of the state's digital infrastructure.
"A state without a secure digital ecosystem will eventually lose its information-technological sovereignty," he said.
According to Mirzayev, the presidential Decree "On defining the Cybersecurity Strategy of the Republic of Uzbekistan and improving the system of preventing cybercrime," adopted in March, became the most important event in the field of cybersecurity. This decree approved Uzbekistan's cybersecurity strategy for 2026–2030. According to the document, government agencies were given the opportunity to use outsourcing services through the private sector. It was also strictly established that commercial banks and payment systems will be directly liable for damage caused to their customers as a result of cybercrimes.
Mirzayev also touched upon practical work and the implementation of laws, recalling that special cybersecurity departments have been established in the central apparatuses of a number of state bodies, the CERT/CBU center regulating the banking sector, a new faculty on digital forensics at the Law Enforcement Academy, a cyber-range complex simulating real cyberattacks at the Academy of the Ministry of Internal Affairs, as well as cybersecurity clubs for youth in the regions.
"One of our greatest technical achievements is the effectiveness of anti-fraud programs in the banking system. These programs, connected to the Central Bank system, stopped 462 billion soums of illegal transfers in real-time as early as the first half of 2026," he said.
At the same time, Mirzayev noted that in recent years, cyberattacks have significantly increased both in terms of quantity and complexity.
"Today, we clearly observe that globally, cyberattacks are forming as a highly automated and systematic industry. In particular, the conclusions of surveys conducted by the World Economic Forum and other international organizations in 2025–2026 clearly demonstrated these global trends. Specifically, 94 percent of respondents pointed to AI as the main threat in cybersecurity, while 73 percent stated they had directly suffered from social engineering and fraud. According to NSA data, the public administration sector has become the main target, with nearly 38 percent of total attacks directed at this field," Mirzayev said.
According to him, the time it takes for attackers to penetrate a network and spread a cyberattack to other systems has shortened to 29 minutes. This means that cyberattacks are fully managed through algorithms and AI is being used as a weapon.
"Attackers use autonomous agents to automatically create targeted phishing, deepfakes, and malicious codes within seconds. At the same time, AI systems themselves are becoming targets of attacks. According to the Avast classification, threats such as injecting hidden commands into an AI model, poisoning data during the model training process, and manipulating highly authorized autonomous agents are among the most pressing problems of today," said the head of the Cybersecurity Center.
Citing official data, Mirzayev stated that over the past five years, the number of cybercrimes in Uzbekistan has increased nearly 11-fold, amounting to more than 62,000 cases. It was established that 82 percent of fraud cases were committed using information technology.
"In order to stabilize the emerging situation and take appropriate systematic measures, mechanisms for early detection, real-time elimination, and response to cyber threats have been formed in our republic through a number of modern technological integrations carried out by relevant state organizations and agencies, as well as innovative monitoring systems developed and implemented directly by local manufacturers. These systems allow for establishing full digital control over the information resources of state bodies and neutralizing external attacks before they lead to negative consequences," Mirzayev said.
It was reported that according to data for 2025–2026, critical information infrastructure objects in sectors of the country such as energy, manufacturing, telecommunications, finance, and education currently remain targets of cyber threats.
"In particular, it was observed that network attacks against the web resources of state and economic management bodies increased by 427 percent compared to the corresponding period of last year. At the same time, the number of cyberattacks from foreign IP addresses on the information systems of state bodies and organizations is growing. In total, botnet networks account for 21.3 percent of cyberattacks, virus activity for more than 56 percent, and attempts to use other types of cyberattacks for 22.7 percent. Within the framework of continuous monitoring of websites in the .uz domain zone, it was recorded that the share of cybersecurity incidents detected this year increased by 570 percent compared to last year," Olimjon Mirzayev said.
Meanwhile, during the past period, the volume of information about cyber vulnerabilities and cyber threats obtained through early detection and warning systems has significantly increased. Based on the analysis of this data, more than 261 million malicious network requests were automatically blocked through web application firewalls. At the same time, over 1.72 billion malicious network requests were neutralized in the networks of a number of organizations connected to centralized protection systems. In addition, more than 50,000 illegal banking operations were stopped, and the leakage of personal data of about 1.5 million citizens was prevented.
In this regard, Olimjon Mirzayev emphasized that in the future, the logic of warfare in cyberspace could change completely.
"We can predict that by 2030, the logic of warfare in cyberspace will change completely. We will have to be ready for an era of struggle where autonomous AI agents adapt to protection systems in real-time, post-quantum threats, and complex attacks launched through the supply chain," he said.
According to Mirzayev, within the framework of the national strategy, Uzbekistan has set clear tasks for itself. In particular, the country plans to integrate algorithms that predict threats in advance into monitoring systems, introduce a national standard corresponding to international requirements, and expand digital forensics capabilities.
At the same time, in the legislative direction, work will continue throughout 2026 on categorizing critical information infrastructures according to their level of risk and introducing a procedure for secure software updates via the Internet. Internet providers will be obligated to filter dangerous traffic.
By the end of this year, as Mirzayev announced, a draft law will be developed to establish liability for officials who are indifferent to security requirements. By 2027, national SOC (Security Operations Center) standards will be approved, and multi-factor authentication will be made mandatory in public services.
The set organizational plans cover all levels of society and the state. By the end of 2026, proposals will be prepared to improve the cooperation environment between the public and private sectors and to establish cyber control within the Armed Forces system.
In addition, work on introducing cyber hygiene classes in schools and signing international agreements on the automatic recognition of foreign security certificates in Uzbekistan will be systematically continued. From the perspective of technological development, local manufacturers of information security tools will be regularly and systematically supported.
"As a logical and largest continuation of these plans, Security Operations Centers, i.e., SOC centers, which automatically predict and respond to cyberattacks across the country, will be fully operational by the end of 2029. Supporting our local vendors based on studying advanced international experience and practices will remain our priority, and of course, to counter global threats, we will further strengthen cooperation with international organizations on exchanging information on current cyber threats. We can build a secure and stable digital future only by relying on technological independence, involving advanced technologies in proactive defense, and expanding international cooperation," Olimjon Mirzayev concluded.