

Websites taken down worldwide as critical cyber-security update issued
The vulnerabilities with PHP, a programming language widely used across the internet, have been described as the most significant ever found by AI.
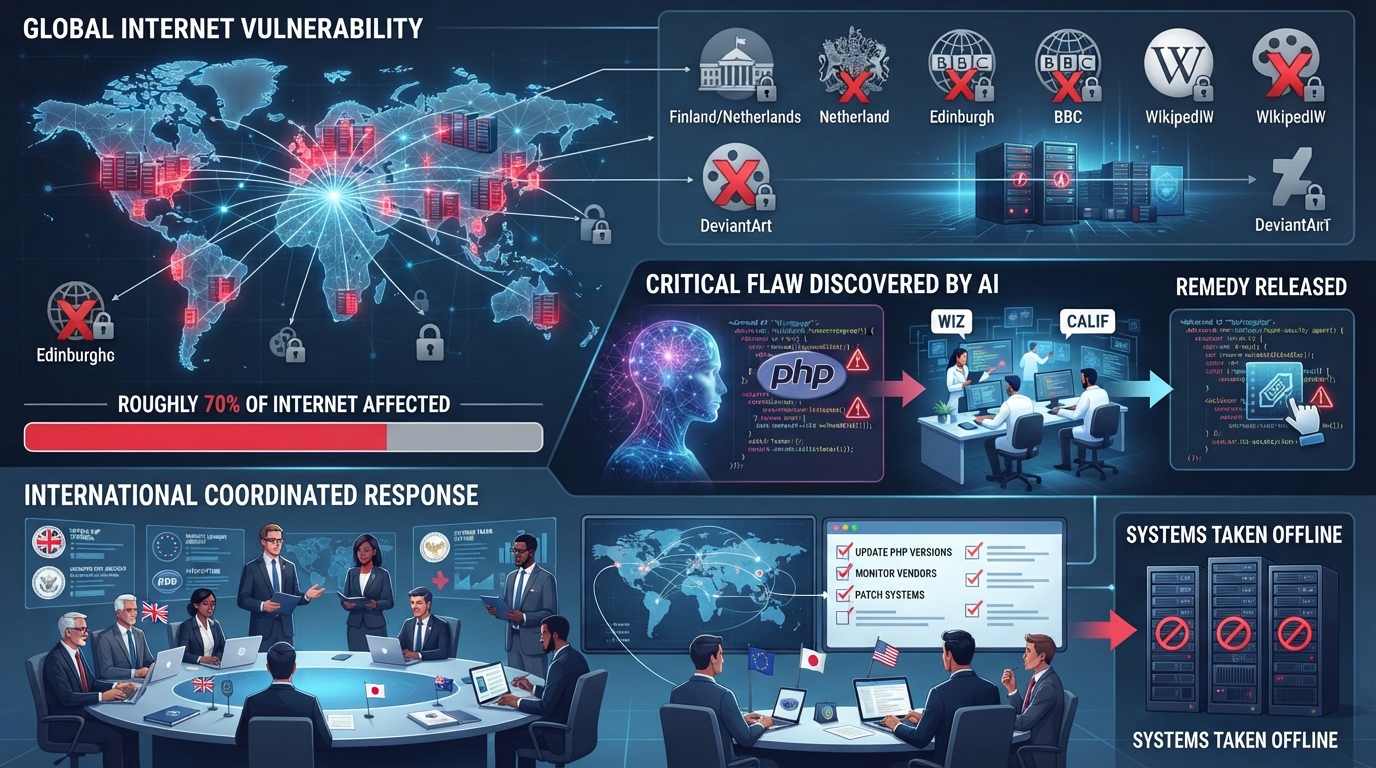
Websites have been taken offline around the world after a critical cyber-security update was released.
Governments and agencies internationally have called on websites to fix two serious cyber-security weaknesses in a programming language that powers much of the internet.
The flaws were identified in the PHP programming language, and a remedy was released on Wednesday afternoon.
Several cyber-security agencies have advised organisations that cannot install the fixes quickly to consider shutting their sites down, prompting bodies including the Finnish government, Edinburgh council and the BBC to take pages offline.
The vulnerabilities were uncovered by AI, with cyber-security company Wiz describing them as the "most severe vulnerabilities ever discovered" by the technology, which is changing the cyber landscape.
Finland has temporarily closed the government's public web services, while the Netherlands' cyber-security agency said it was taking its own website offline because of the vulnerabilities.
"These vulnerabilities often provide a direct path to the server's file system or database," it wrote.
Meanwhile, the White House said federal agencies were working with leading AI labs to accelerate a fix to the problem.
Japan's Prime Minister Sanae Takaichi urged people to check whether their publicly available websites were running on PHP.
The Wikimedia Foundation, which operates the online encyclopedia Wikipedia, said it was dealing with the security flaws.
"We have taken down a number of other systems as a precautionary measure until they can be safely patched," it said.
As a result, some people were unable to access parts of Wikipedia on Wednesday.
Edinburgh council's website has also become inaccessible, along with the online homes for several BBC programmes including Doctor Who and The Traitors.
Other websites, including the art platform DeviantArt, have said they are "temporarily down for maintenance".
The vulnerabilities were found by cyber-security researchers at the firms Calif and Wiz.
Calif, together with PHP Foundation, took part in a programme launched by OpenAI called Patch the Planet.
Through that programme, they were given access to the AI company's advanced tools to search for and repair flaws in the web development language.
It added that an internal researcher at the company had also found the issue at around the same time as the other firms.
The flaws had gone unnoticed for more than a decade. By August, after a few weeks of using advanced AI tools, they were discovered.
"Frontier models were critical to making this process practical, enabling us to develop and adapt working exploits across multiple applications in hours," Wiz said in a blog post.
It has estimated that "roughly 70%" of the internet is affected, although the BBC is unable to verify that figure.
Although PHP Foundation had planned to announce its discovery later this month together with a full fix for the problem, usually called a "patch" by software developers, details of the flaw were leaked on social media on Tuesday.
That forced PHP Foundation to rush out its announcement of the vulnerability and its enormous scale.
The Netherlands' National Institute for Public Health and the Environment, an agency of the Dutch government, has taken down its website.
Likewise, the website of the Tweede Kamer, the lower house of the country's parliament, has become inaccessible.
The UK's National Cyber Security Centre (NCSC), along with its counterparts in the EU and Australia, has urged PHP users to apply the fixes.
"Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated," the NCSC said in a note.
Japan's national cyber-security office and EU cyber-security officials have issued a similar warning.
"PHP is everywhere. It quietly powers WordPress, Drupal, Joomla, and Magento sites, shared hosting platforms, control panels, and an awful lot of software that doesn't even advertise that it runs PHP under the hood," cyber-security company Huntress said.
Cyber-security expert Don Smith, from the Sophos Counter Threat Unit, told the BBC this would "likely be a priority target" for hackers.
He said the immediate challenge was not just installing a patch to fix the issue, but locating and managing every instance where PHP was running.
"The use of PHP is pervasive, it can sit beneath public websites, content management systems, hosting platforms and third-party products, sometimes without even being obvious to the organisation using it," he said.
He said it was vital that organisations watched for signs that an attacker "might have already have gained a foothold".
The European Union Computer Emergency Response Team (CERT-EU) said the risk scores assigned to the vulnerabilities "indicate the potential for unauthenticated remote code execution".
Such a cyber-attack could potentially let hackers install malware and bring down websites.
Dane Knecht, chief technology officer at internet infrastructure firm Cloudflare, said he was
The NCSC said that once organisations have installed the update, they should "continuously monitor for security updates from third-party software vendors, including for appliances and services that may bundle PHP".
It is not yet clear which versions of the programming language are affected, but CERT-EU said it could impact all versions dating back to PHP 5 onwards - which launched in 2004.
The PHP Foundation has issued the update only for the latest versions, however, with people using PHP 8.1 or older urged to upgrade.
PHP was created for web development. It is used on servers to produce what you see when you visit websites.
Not all websites use it, but it still powers a large share of the internet.