

Requirements against fraud in remote financial services will be tightened
Customers will be provided with the opportunity to independently block and unblock any portion of the funds in their account
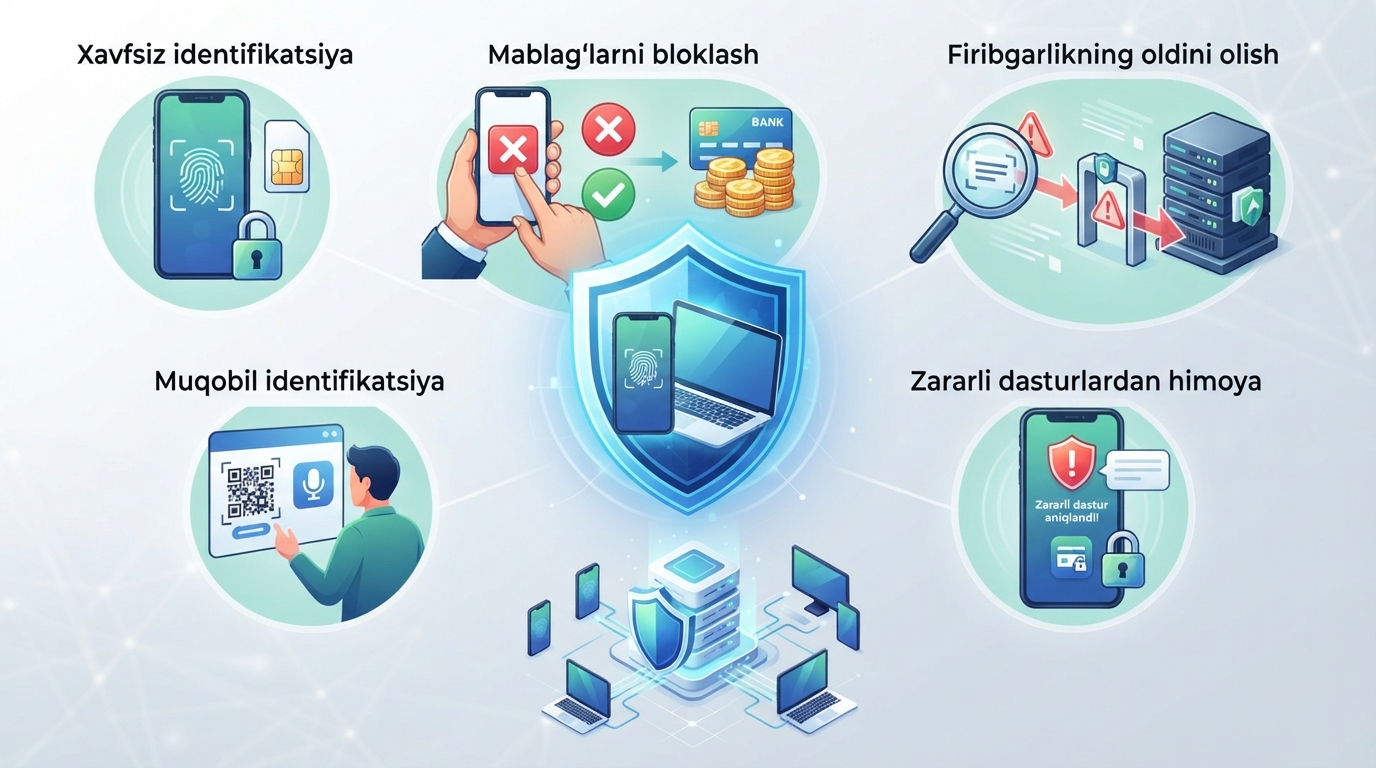
Anti-fraud requirements in remote financial services to be tightened
The Central Bank has drafted a decree to improve the minimum requirements aimed at ensuring cybersecurity and preventing fraud in remote financial services.
The draft provides for the following key changes:
"Secure Identification."
Using biometric identification and device-bound verification methods in addition to SMS codes.
"Blocking Funds."
Creating an opportunity for customers to independently block and unblock any portion of funds in their account.
"Fraud Prevention."
Introducing a procedure for temporarily suspending suspicious transactions.
"Protection Against Malware."
Notifying the customer within one hour if malware is detected on their device and restricting critical operations.
"Alternative Identification."
Applying other verification methods for citizens who are unable to pass biometric verification.
In addition, an obligation is established for banks to notify the Central Bank of cyber incidents within 24 hours, along with liability regarding the security of data exchange with partner organizations.
The draft decree can be reviewed and feedback left via "regulation.gov.uz" (the portal for discussion of draft legislative acts).