

Binance says fake job interviews used as part of $6.3bn crypto hack
An engineer was contacted through a legitimate job-hunting platform and invited to bogus job interviews with fake company representatives, Binance says.
Binance says fake job interviews used as part of $6.3bn crypto hack
Hackers who stole a record $6.3bn (£4.7bn) from Binance used fake job interviews and a compromised internal AI tool, the company has said.
Initial findings released by the firm, which runs the world’s largest cryptocurrency exchange, said the hackers accessed its systems through a “sophisticated, multi-stage campaign”.
It said they used a variety of methods, including malicious software downloads, to infect the computers of Binance engineers and take control of tools used to drain billions of dollars’ worth of crypto from its wallet.
Binance described the breach as a “serious and highly sophisticated security incident” and apologised, saying “this should not have happened”.
Binance said the hackers had targeted its engineers with social engineering tactics.
These involve methods such as phishing, where hackers try to trick people into revealing sensitive or personal information that can then be used to access their accounts.
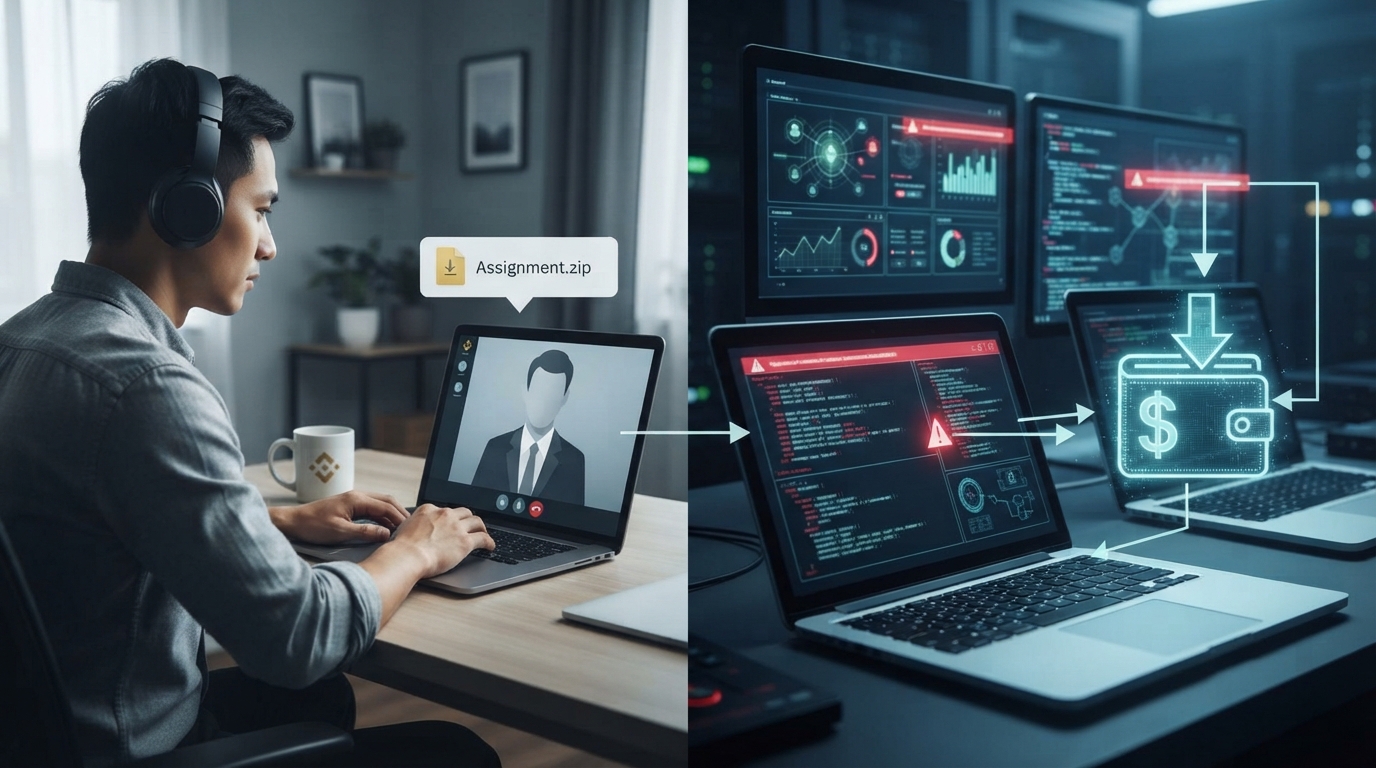
Binance said that as part of the attack, one of its engineers was approached via a legitimate job-hunting platform and invited to fake job interviews with bogus company representatives.
It said the attackers used “more advanced and deceptive” techniques to gain his trust, including sharing social media accounts containing personal photos.
During a second interview, the engineer was told to download malware disguised as an “assignment”, which installed malicious code using “obfuscation techniques” to avoid detection.
Binance said the hackers then used the engineer’s compromised computer and a compromised internal AI tool in October to take control of two other engineers’ laptops and carry out the next stages of the attack.
The incident forced Binance to suspend withdrawals for customers worldwide, meaning users could not move their cryptocurrency off the platform until services were restored on Sunday.
Customers withdrew billions of dollars’ worth of assets after the platform reopened.
“We apologise for the concern, disruption and uncertainty it caused our users, partners and the wider industry,” it said.
The company added that it had taken several steps after the incident, including working with law enforcement to trace and freeze affected assets.
It said it had also set aside more than 100% of the funds needed to cover the loss, and noted that 98% of the token assets affected had been “replenished” by Saturday.
The record $6.3bn (£4.7bn) attack is believed to be the biggest crypto hack so far.
US crime agencies, including the Federal Bureau of Investigation (FBI) and Secret Service, have been helping Binance trace the crypto taken from the platform’s own wallets.
The agencies, together with a range of cyber analysts, said the hack — like similar breaches before it — showed signs of having been carried out by North Korea.
Kim Yo Jong, a senior Democratic People’s Republic of Korea official and sister of leader Kim Jong Un, said the accusations were another “sinister attempt” by the US to damage North Korea’s public image.
The country has repeatedly denied involvement in a number of major cyber attacks it has been accused of in recent years.
The TraderTraitor unit, also known as the Lazarus Group, was blamed for a then-record $1.5bn hack of crypto exchange Bybit in 2025.
Binance had previously not responded to the BBC’s questions about North Korea’s alleged role in the hack.
But on Tuesday, the company wrote on X, external: “The latest information released by the Federal Bureau of Investigation indicates that the Democratic People’s Republic of Korea is responsible for this incident.”
As part of its security response after the attack, Binance said it would also increase investment in AI tools that can detect security threats, and bring in third-party cyber experts to conduct a full review of the incident.
It also said it would seek to establish a security research fund and work with leading AI and security firms on targeted initiatives.